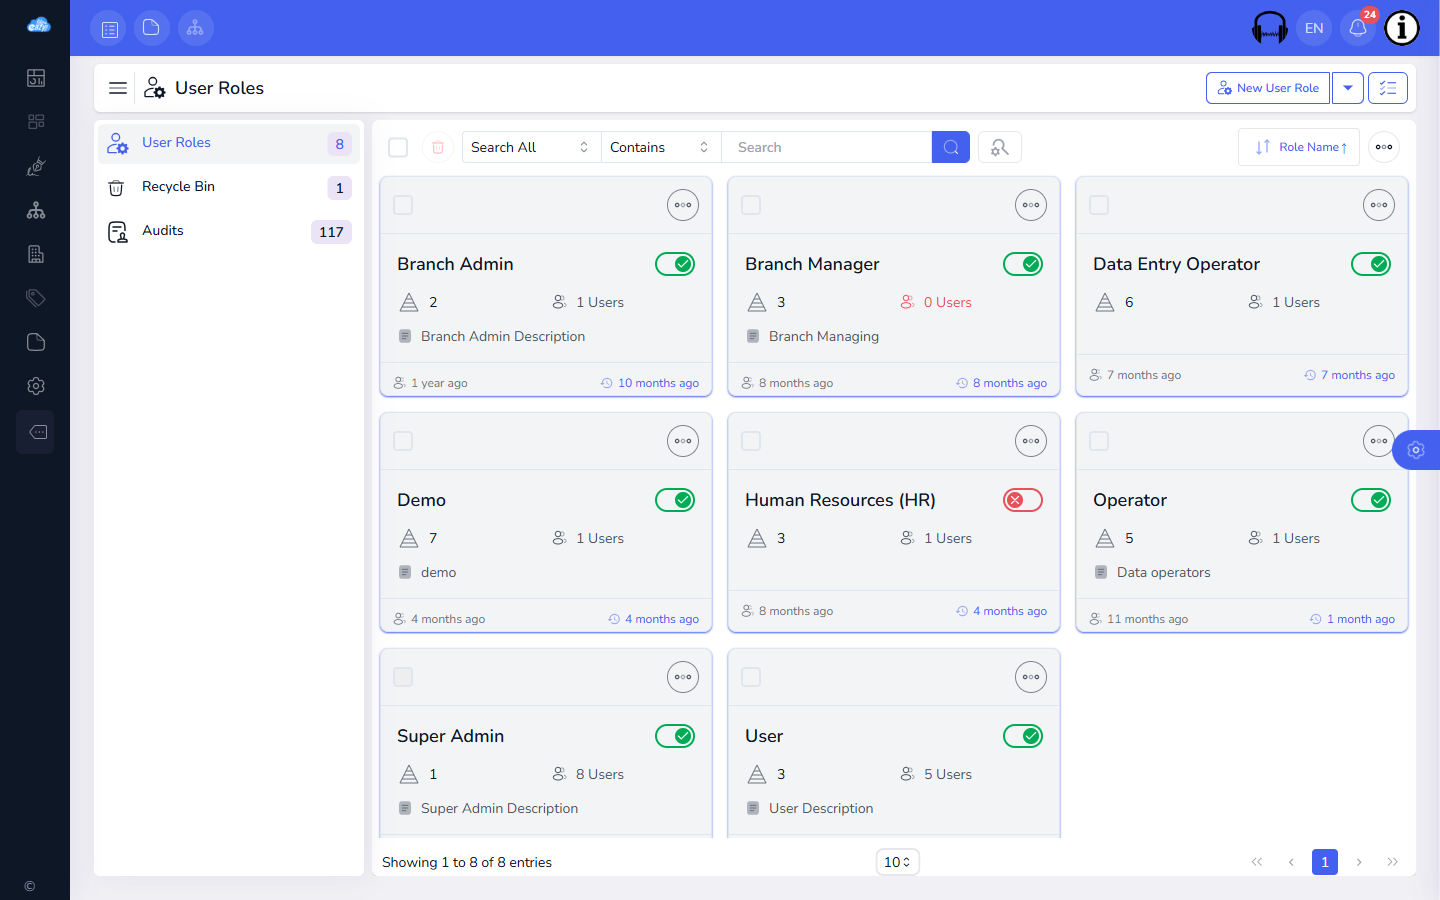
Access in FileEazy is controlled through roles, applied at the level of the workspace, branch, department, folder or individual file, so a user's role determines exactly what they can see and change, and nothing more.
The alternative, giving everyone broad access and trusting them not to look at what isn't theirs, doesn't hold up for compliance or for basic data hygiene as a team grows. Scoped roles enforce that boundary structurally instead of by policy alone.
We use necessary cookies to run the site and remember your language and currency. With your consent we also use analytics cookies to see how the site is used, and load the Google Maps embed on our contact page.
Read our Privacy Policy
30% OFF
Limited time
30%off
30% off your first year
Our launch offer runs until 31 October on all annual plans. Enter the code at checkout and it applies to your whole first year.